cybersecurity|cyberthreats
WoW: Forever hype fuels rapid surge in malicious domains
The announcement of World of Warcraft: Forever at BlizzCon 2026 didn't just get fans excited; it sent scammers straight to work, too. In the weeks following the game’s reveal, Surfshark tracked 147 new WoW: Forever-themed domains, a surge that doubles the pace of malicious activity seen after the GTA 6 announcement. These fraudulent sites are designed to exploit decades of player habits, baiting fans with promises of free beta access and unauthorized gold-selling workarounds. Ultimately, these lures serve as a front for harvesting sensitive account credentials and credit card information from the community.
Worst of all, this initial wave appears to be only the beginning. The velocity of new domain registrations is accelerating rapidly, suggesting that scammers are scaling their efforts to meet the growing hype. As the game approaches its release date, we expect these scam tactics to become even more sophisticated, targeting the influx of returning veterans and new players who may be less familiar with Blizzard's official distribution channels.
Key insights
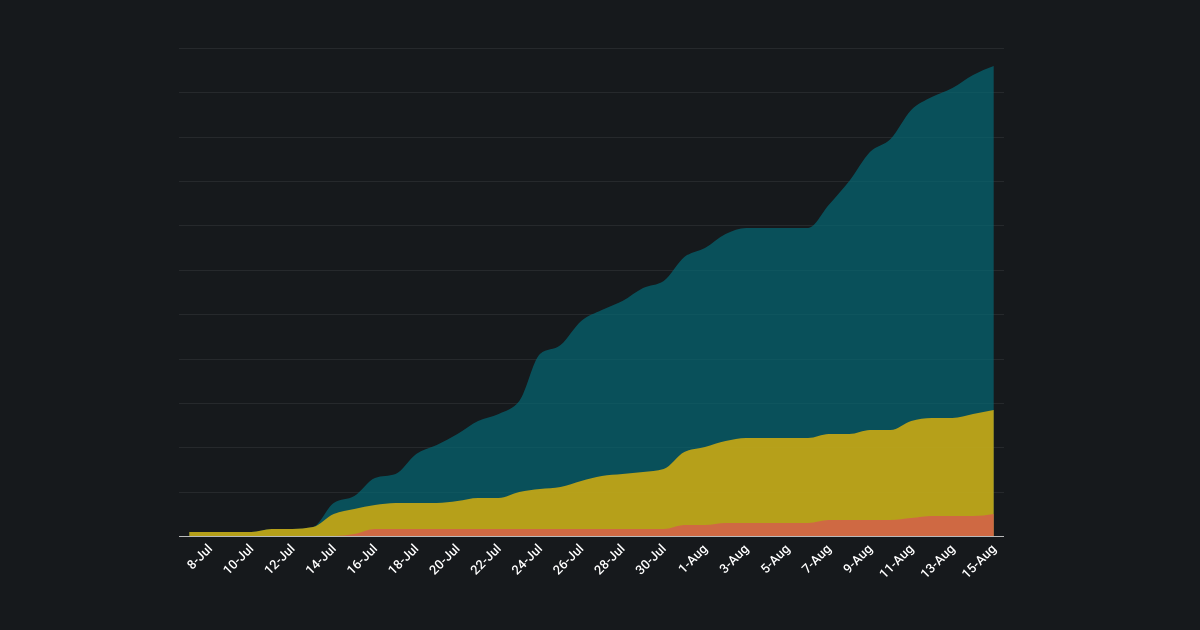
- World of Warcraft: Forever was announced at BlizzCon on September 12, 2026, and those registering lookalike domains moved quickly. By the following day, 23 new domains had already appeared, making it the single busiest day in the entire data collection window. A second wave of 22 more arrived on September 17, the day the beta went live. In total, 147 WoW: Forever-themed domains appeared in just 15 days, at a rate of roughly 10 per day — nearly double the pace recorded ahead of GTA 6 at a comparable stage.¹ The pattern suggests domain registrations track major game milestones rather than building gradually, and the bigger the moment, the faster they appear.
- Around one in six of these domains appear to be built to defraud players, with a dominant lure unique to WoW. In-game gold selling accounts for 12 of the 25 scam-intent domains, a scam type with no real equivalent in other game launches. On September 17 alone, nine nearly identical gold-related domains were registered simultaneously across multiple extensions. Registering the same core name across multiple extensions at once can be a sign of an organized operation rather than an opportunistic individual. It also exploits a cultural reality specific to WoW: players have traded in-game currency through unofficial channels for decades,² and that familiarity makes them more likely to trust what they see.
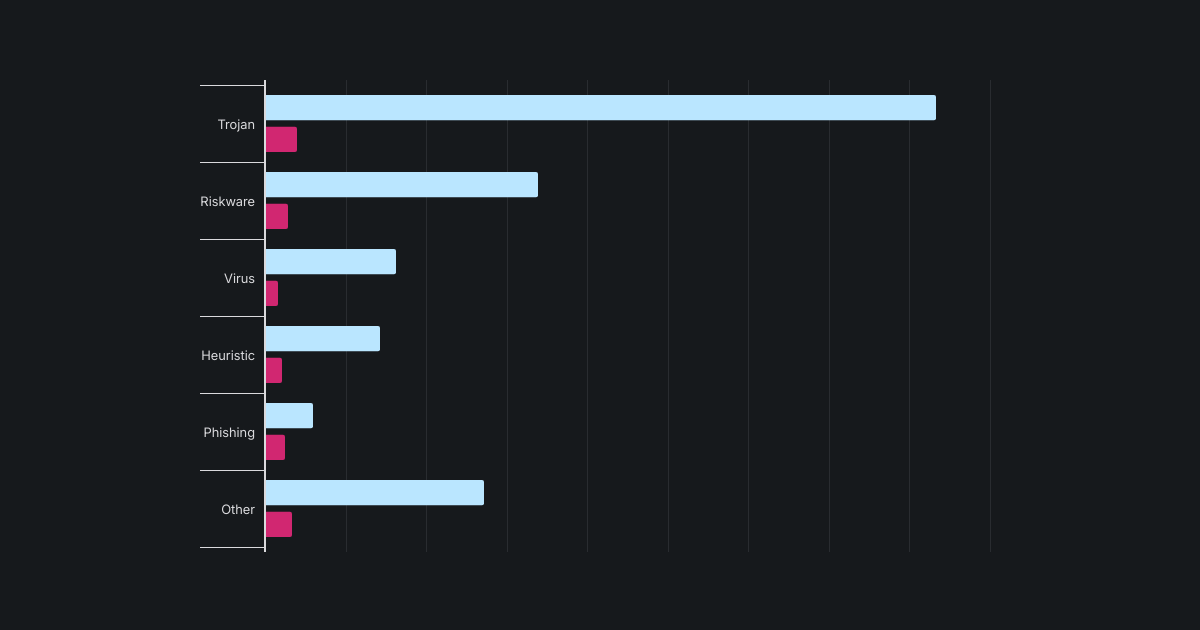
- Independent checks on VirusTotal³, which aggregates verdicts from dozens of security vendors, already flagged four domains as malicious, phishing, or suspicious. What makes this particularly striking is that none of the four have names that would raise immediate suspicion. At first glance, they look like any other fan site or community page. Confirmed threats do not always advertise themselves, and the most dangerous domains are often the ones you would not think twice about clicking.
- The beta period is an especially dangerous window, and the data bears this out. The first beta-themed domain appeared on September 21, four days into the real beta, likely targeting players who had not been granted access and were looking for a way in. Beta phases concentrate risk: demand is high, legitimate supply is deliberately limited, and the gap between the two is exactly where scammers operate. The same dynamic was documented ahead of GTA 6, where fake beta key sites were among the earliest scam types to emerge.
- If the current pace holds, more than 500 WoW: Forever domains could be registered by launch day on November 4, more than triple the current total and more than the entire GTA 6 count recorded over a much longer window. But the headline number at freeze is not the real warning. As with GTA 6, the larger threat is not how many domains exist today, but what happens when they are switched on. Scam infrastructure tends to activate around launch rather than register around it, meaning many of these domains could be sitting ready and waiting for the moment player traffic peaks.
Methodology
Domain data was collected using the WhoisXML API Brand Alert service⁴, which returns newly registered domains matching a given brand term, each with a registration date and a status flag. Following the BlizzCon 2026 announcement on September 12, daily collection began on September 13 and ran until a data freeze on September 27, 2026. Queries used the primary brand token "wowforever", with "wowforeverbeta" and "foreverwarcraft" checked separately, and excluded fan-content noise as much as possible. Each domain was kept only if it was a valid hostname and newly registered or newly detected in the source data. Pre-existing and deleted domains were excluded, and the final set was de-duplicated to unique domains.
Scam-intent classification used a keyword-based rule set adapted from our GTA 6 domain study¹ to reflect WoW-specific threat types, including in-game gold selling, fake servers, fake beta access, and private server lures. A broader query covering the period before the BlizzCon announcement returned a higher total domain count, suggesting registrations were already underway before the reveal and accelerated afterward. However, the pre-announcement set falls outside the API's retrievable window.
All figures reflect a pre-launch snapshot gathered ahead of the game's November 4, 2026 release. Domains were also independently cross-checked against VirusTotal, which aggregates verdicts from dozens of security vendors, to identify confirmed active malicious or phishing activity.
For the complete research material behind this study, click here.